Identity & Access Management
Most breaches involve a valid login used by the wrong person. We build identity programs around single sign-on, phishing-resistant authentication and least privilege, so access is granted deliberately and removed promptly.
Scope
What is included
The right people, the right access, verified every time.
Single sign-on
One identity for workforce applications, with access tied to role.
Phishing-resistant MFA
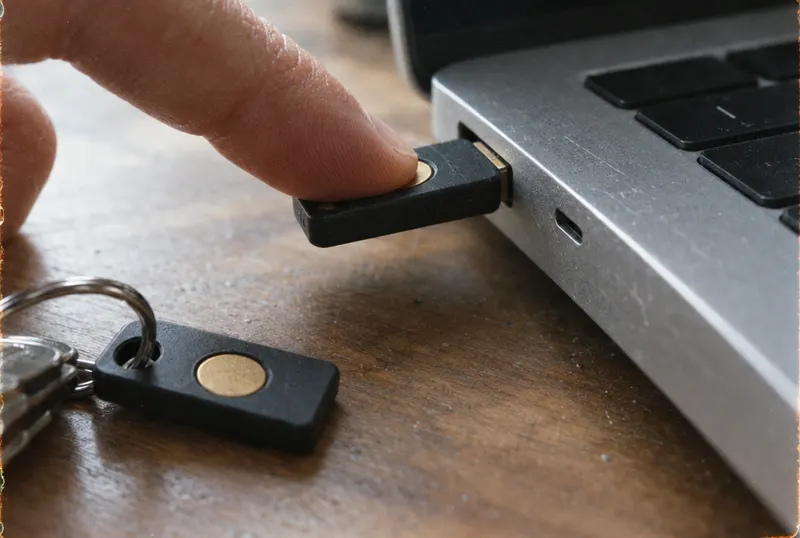
Hardware security keys and passkeys for staff and administrators.
Privileged access management
Vaulted, time-limited and recorded access to critical systems.
Joiner, mover, leaver automation
Accounts created, changed and removed from HR events, not tickets.
Access reviews
Quarterly certifications with evidence ready for audit.
Zero trust network access
Application-level access that checks user and device on every request.
Method
How it works
Three stages, each with a written output, so you always know what has been done and what comes next.
- 01
Map
We chart who has access to what and where the risky gaps are.
- 02
Consolidate
Applications move behind single sign-on and strong authentication.
- 03
Govern
Reviews, automation and privileged access controls keep it clean.
Standards and technology
Do staff really need hardware keys?
For administrators and anyone handling money movement, yes. Codes sent by text or app can be phished; hardware keys and passkeys cannot be relayed to a fake site.
Can you work with our current identity provider?
Yes. We work with the major identity platforms and can improve what you have before suggesting any change.
How do access reviews work?
Managers receive a list of their team's access each quarter, approve or revoke in a few clicks, and the decisions are recorded as audit evidence.
Related